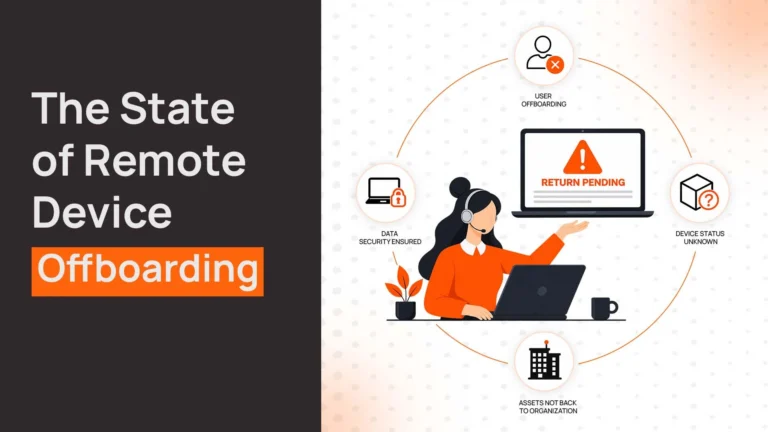
Remote employee offboarding looks simple on paper: disable the employee’s access, get the laptop back, wipe it, and close the asset record.
In practice, each of those steps can fail independently.
There is no physical handoff at the office. The employee may be working from another city or country. IT may manage identity through one system, VPN through another, the laptop through an MDM platform, and hardware retrieval through email and a courier. If those pieces are not connected, an offboarding that should take a few hours can turn into days of follow-ups and uncertainty.
A structured remote employee offboarding checklist solves much of that problem by making the sequence explicit.
The important part, however, is not simply having a checklist. It is following the right order: secure access first, protect the device and its data, initiate retrieval, verify the return, and document what happened.
This guide gives IT, Security, HR, and Operations teams a practical process they can adapt to their own environment.
Why Remote Offboarding Breaks Down Differently Than In-Office Offboarding
An office-based employee usually creates a natural physical handoff. They walk into the office, return the laptop, hand over their access card, and leave the company’s physical environment. Even when the formal process is imperfect, the physical workplace provides a degree of control.
Remote work removes that forcing function.
The laptop may be sitting in an employee’s home hundreds or thousands of kilometres away. There may be no IT employee nearby, no office receptionist to receive the equipment, and no convenient moment when someone can physically confirm that the device has been returned.
That makes remote device offboarding both a security process and a logistics process.
There is another complication: access is rarely limited to email. A departing employee may have access to:
- SSO and identity systems
- Email and collaboration tools
- VPN or Zero Trust access
- SaaS applications
- Cloud platforms
- Shared accounts
- Administrative tools
- API keys or service credentials
- Company-owned devices
Sequentur’s current remote offboarding guidance specifically highlights the need to handle Microsoft 365 access, VPN and other remote-access channels, shared credentials, device recovery and documentation as separate parts of the process.
For remote teams, therefore, “disable the employee” is not one action. It is a sequence of actions that need clear ownership.
The Remote Employee Offboarding Checklist, In Order
The following sequence is designed to reduce the two biggest risks during remote offboarding: continued access and unrecovered equipment.
Use it as a working checklist and adapt the exact timing to your company’s security policy, employment arrangements and the nature of the departure.
1. Coordinate HR and IT Before the Exit
The offboarding process should begin with coordination between HR, IT, Security and the employee’s manager.
Before the exit conversation, confirm:
- Employee’s final working date and time
- Whether the departure is voluntary or involuntary
- Employee’s current location
- Devices assigned to the employee
- Personal devices used under a BYOD policy
- Systems and applications requiring access removal
- Manager responsible for knowledge transfer
- Whether the employee has elevated or administrative access
- Return address or preferred retrieval location
This is especially important for involuntary departures, where the timing of access removal may need to coincide with the termination conversation.
Sequentur recommends gathering device assignments, shipping information, shared credentials and application ownership before starting the offboarding process rather than discovering those details after the employee has already left. Where HRIS integration exists, this handoff can be triggered automatically rather than depending on someone remembering to send an email.
Checklist:
☐ HR has confirmed the departure
☐ IT/Security has been notified
☐ Final working time is confirmed
☐ Assigned hardware has been identified
☐ Employee location is confirmed
☐ Special access or privileged accounts are flagged
2. Revoke SSO and Email Access
Once the employee’s access removal window begins, identity access should be addressed immediately.
At a minimum, review:
- SSO account
- Corporate email
- Active sessions
- Authentication tokens
- MFA methods
- Directory access
- Cloud applications connected through the identity provider
For example, Sequentur’s Microsoft 365 guidance recommends blocking sign-in, revoking active sessions, resetting the password and removing registered MFA methods as part of the initial access-control sequence.
The exact controls will depend on your identity platform, but the principle is universal:
Do not assume that disabling one login automatically closes every active session or application connection.
For sensitive or involuntary departures, Security may also need to preserve relevant logs before accounts are fully decommissioned.
Checklist:
☐ SSO access revoked
☐ Email access disabled
☐ Active sessions terminated
☐ Authentication tokens reviewed/revoked
☐ MFA methods removed
☐ Application access reviewed
3. Revoke VPN and Other Remote Access Separately
This deserves its own step.
A common mistake is assuming that disabling SSO automatically handles every remote-access mechanism. It may. It may not.
Depending on your environment, review:
- VPN
- Zero Trust Network Access
- Remote Desktop
- Virtual desktop environments
- SSH or jump-host access
- RMM platforms
- Firewall exceptions
- Administrative portals
Sequentur explicitly treats VPN, ZTNA, remote desktop, jump hosts and remote-support tools as separate access channels that should be checked rather than assumed to be covered by Microsoft 365 or another identity system.
Checklist:
☐ VPN disabled
☐ ZTNA policies reviewed
☐ Remote desktop access revoked
☐ Server or SSH access removed
☐ RMM access removed where applicable
☐ Firewall exceptions reviewed
4. Rotate Shared Credentials
Individual accounts are easier to disable than shared credentials.
If the departing employee knew a shared password, API token, recovery code or other credential, removing their personal account does not necessarily remove their ability to use that credential.
Identify any shared access associated with the employee and rotate credentials where required. This may include:
- Shared inbox credentials
- Admin passwords
- Service accounts
- API keys
- Cloud credentials
- Database credentials
- Vendor portals
- Emergency access codes
The exact scope depends on the employee’s role. An engineer, finance administrator and customer-support employee will not create the same credential exposure.
Checklist:
☐ Shared passwords identified
☐ Privileged credentials reviewed
☐ API keys reviewed
☐ Service-account access reviewed
☐ Required credentials rotated
5. Wipe the Company Device Remotely
This is where the order of operations matters.
If the company laptop is enrolled in an appropriate MDM or endpoint-management system, IT may be able to initiate a remote lock or wipe without physically possessing the laptop.
That means there is often no operational reason to wait until the device arrives at a warehouse before protecting company data. The exact capability depends on the operating system, MDM configuration, device state and whether the laptop can receive the management command. A remote wipe should therefore be treated as a control within a broader device-security process, not as a guarantee that every device can always be erased instantly.
For devices that are offline, the command may not execute until the device reconnects.
The key distinction is: Data protection and physical recovery are two different jobs.
A remote wipe can help protect corporate information. It does not bring the laptop back. If you are evaluating tooling for this step specifically, our guide to laptop recovery software for offboarding compares what each category of tool actually handles.
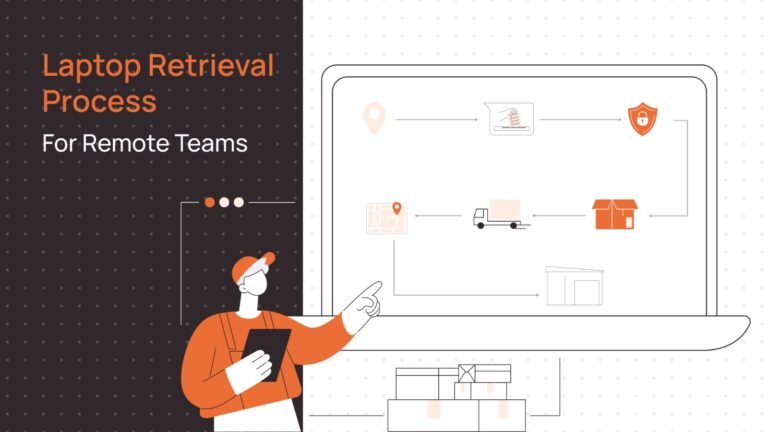
6. Send a Prepaid Return Kit or Shipping Label
Once access has been secured, make the physical return as easy as possible. A good return process should tell the employee exactly:
- What needs to be returned
- Where it needs to go
- How it should be packaged
- Who pays for shipping
- When it needs to be returned
- How the shipment should be tracked
For laptops, the return kit may include:
- Appropriate packaging
- Protective material
- Prepaid shipping label
- Return instructions
- Asset or ticket reference
- List of equipment expected back
Sequentur recommends using a prepaid return kit or label and tracking the shipment so the organization has a verifiable record of the return. This small operational detail matters because every additional action required from a former employee creates another opportunity for the return to stall.
Checklist:
☐ Return instructions sent
☐ Prepaid label or return kit arranged
☐ Deadline communicated
☐ Equipment list included
☐ Tracking reference recorded
For a deeper look at the physical recovery side, see our complete guide to remote employee laptop return for IT teams.
7. Track the Shipment Until the Device Arrives
Sending the label is not the end of the process. The IT or Operations team should know whether the device has:
Not shipped → Shipped → In transit → Delivered → Received → Verified
That status should live in the same asset record wherever possible. For international employees, tracking becomes even more important because the shipment may involve multiple logistics providers, customs clearance and longer transit windows. A device marked “return requested” is not the same thing as a device physically recovered.
That distinction matters when reporting recovery rates and asset availability.
8. Verify the Device When It Arrives
When the laptop arrives, do not simply mark the ticket as complete.
Verify:
- Serial number
- Asset tag
- Device model
- Charger and accessories
- Physical condition
- Return date
- Data-wipe status
- Any reported damage
The serial number should match the device assigned to the employee. This prevents a surprisingly simple problem: closing the wrong asset record because the return was tracked only through a shipping reference. Sequentur recommends verifying the returned contents against the equipment list and confirming the serial number when the device arrives.
Checklist:
☐ Device received
☐ Serial number verified
☐ Asset tag verified
☐ Accessories checked
☐ Physical condition recorded
☐ Return date recorded
9. Document the Entire Offboarding Record
The final step is not “laptop received.” It is documentation. Six months later, the company should be able to answer:
- When was access revoked?
- Who performed the action?
- When was the device wipe initiated?
- Did the wipe complete?
- When was the device returned?
- What condition was it in?
- What happened to the device afterward?
This matters for internal accountability as much as it does for formal compliance requirements. Sequentur recommends retaining timestamps for access revocation, device return, wipe logs, data-disposition decisions and other relevant offboarding actions.
CheckFlow’s 2026 offboarding guidance similarly treats access revocation, device recovery, data ownership and audit trails as connected parts of a complete IT offboarding process.
Checklist:
☐ Access revocation recorded
☐ Wipe action recorded
☐ Return tracking recorded
☐ Serial number confirmed
☐ Device condition recorded
☐ Final disposition recorded
☐ Exceptions documented
10. Decide What Happens to the Device Next
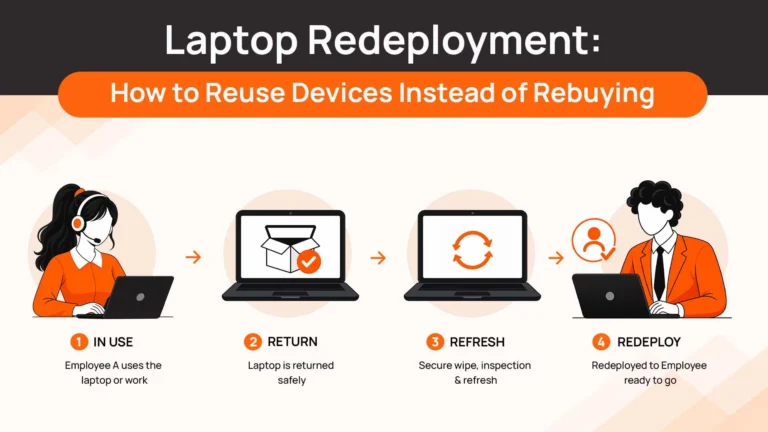
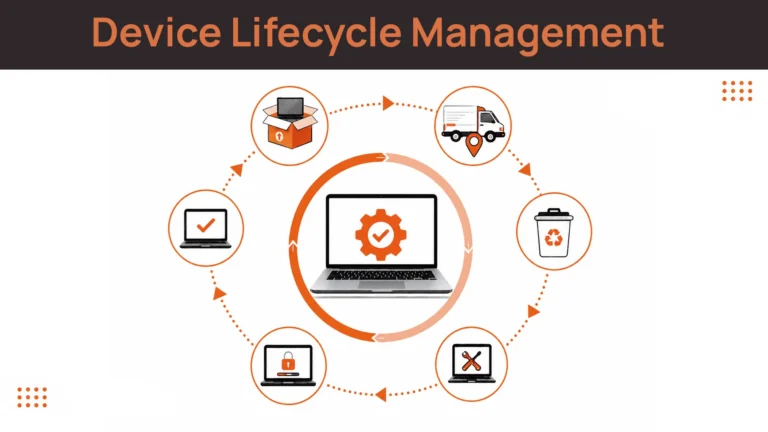
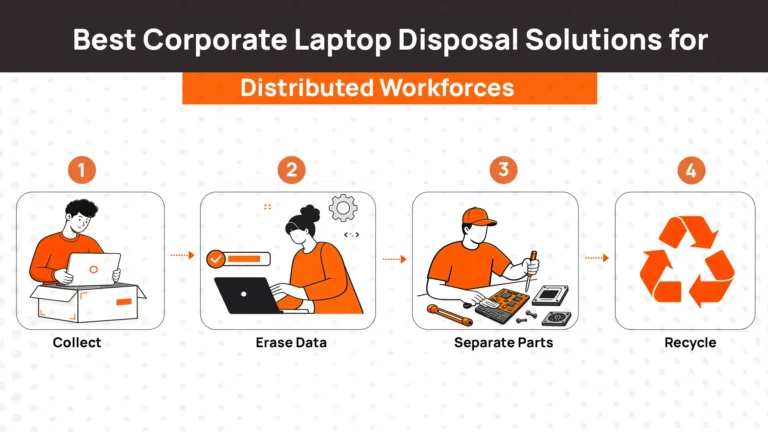
Getting the laptop back is not the end of its lifecycle. Once the device has been received and appropriately sanitized, decide whether it should be:
- Redeployed
- Repaired
- Refurbished
- Stored as spare inventory
- Resold
- Recycled
- Disposed of through an appropriate ITAD process
This is where offboarding connects directly with device lifecycle management.
If the device is still suitable for another employee, immediately replacing it with a new laptop can create unnecessary hardware expenditure.
Our guide on how to refurbish and redeploy company laptops when employees leave covers this next stage in detail. If the device has reached the end of its useful life, see our corporate laptop disposal guide for the broader disposition decision.
Related Reads
Each stage of this checklist has a deeper guide if you need to build the process rather than just run it once:
- Complete Guide to Remote Employees Laptop Return for IT Teams — the retrieval half of this checklist, in full.
- Best Laptop Recovery Software for Offboarding — what the tooling in steps 5 to 7 actually does and does not cover.
- Best Tools to Automate Laptop Onboarding and Offboarding — for turning this checklist into a triggered workflow.
- Best Employee Equipment Return Services for Remote Teams — chargers, monitors and docks, which most return processes forget.
- What Happens If You Keep a Company Laptop After Leaving? — the non-return scenario from both sides.
- How to Refurbish and Redeploy Company Laptops When Employees Leave — where the device goes once step 10 says “reuse.”
The Two Mistakes That Cause the Most Trouble
Mistake 1: Waiting for the Laptop Before Protecting the Data
One of the biggest process errors is treating physical recovery as a prerequisite for data protection.
If a company-managed laptop can receive a remote lock or wipe command, IT can potentially protect corporate data before the device is physically returned.
That does not eliminate the need to retrieve the hardware. It simply means the security process does not have to wait for the logistics process. The two workflows should run in parallel.
Access protection → remote device controls → physical retrieval
rather than:
Wait for laptop → receive laptop → start thinking about security
Mistake 2: Assuming SSO Revocation Covers Everything
SSO has made access management significantly easier, but it should not create a false sense of completeness. VPN access, privileged credentials, shared passwords, API keys, remote desktop access and other systems may require separate actions depending on the company’s architecture.
That is why a good offboarding checklist should list the actual access channels instead of simply saying:
☐ “Disable employee”
The more distributed the company’s technology stack, the more important this distinction becomes.
What If the Device Doesn’t Come Back?
A good process should already have an escalation path. The first step should usually be a clear reminder rather than immediate escalation. A practical sequence could look like:
Return request → Reminder → Second follow-up → Manager/HR escalation → Formal recovery process
The exact escalation should depend on company policy, employment agreements and applicable law. HR and legal teams should determine what actions are permissible in the relevant jurisdiction. The important thing for IT is to document each stage.
Record:
- Date of the original request
- Return deadline
- Reminder dates
- Employee responses
- Tracking information
- Manager or HR escalation
- Final outcome
The device should also already be protected through the company’s available endpoint controls where technically possible. That changes the risk profile.
Instead of simultaneously dealing with an unsecured company device and an uncooperative former employee, the company is primarily dealing with an asset recovery problem.
For a deeper look at this scenario from both the employee and employer side, see What Happens If You Keep a Company Laptop After Leaving?.
What Changes for International Employees?
International offboarding introduces another layer of complexity. A former employee may be willing to return the laptop, but the physical process can still take longer because of:
- Cross-border shipping
- Customs requirements
- Local courier availability
- Different return addresses
- Higher shipping costs
- Regional holidays
- Time-zone differences
This is why global companies should not design their offboarding process around a single domestic return workflow. A return process that works perfectly for an employee in New York may be inefficient for someone leaving from Singapore, Berlin or Mumbai. For distributed teams, local retrieval options can reduce the number of international shipping steps involved.
Our guide to the best international laptop retrieval services for remote teams goes deeper into the operational considerations.
A Note on BYOD
Bring Your Own Device requires a different offboarding process because the hardware belongs to the employee.
The company should not treat a personal laptop in the same way as company-owned equipment.
Instead, the organization needs to determine what corporate data, accounts and applications exist on the device and what controls are available under its BYOD policy.
Depending on the technology being used, that may involve removing corporate accounts, revoking access, deleting managed applications or using selective data removal rather than wiping the entire device.
The exact process should be defined in the company’s BYOD policy before the employee leaves.
The important distinction is simple:
Company-owned device: recover and securely sanitize the device according to policy.
Employee-owned device: remove or protect corporate data and access without treating the employee’s personal hardware as company property.
How Remoasset Can Simplify Remote Device Offboarding
The biggest problem with remote offboarding is often not that individual tasks are technically difficult.
- It is that the tasks are spread across different systems and different people.
- HR knows when the employee leaves.
- IT knows how to revoke access.
- Security manages device controls.
- Operations may coordinate shipping.
- Asset management tracks the laptop.
- Finance may need the final asset status.
A connected workflow can reduce the amount of manual coordination required between those teams.
With Remoasset, the offboarding process can connect the employee event with the physical device workflow, including retrieval coordination, asset tracking and the next lifecycle decision. Instead of creating a new email thread every time someone leaves, the device can remain tied to a structured lifecycle record.
That matters particularly for distributed teams where the employee, IT team, retrieval location and final device destination may all be in different places. The objective is not to remove human judgment from offboarding.
It is to make sure the routine steps happen consistently, in the right order, without relying on someone remembering to start them. If you want to see that sequence running end to end, book a demo.
The Checklist Works Because of the Order
A remote employee offboarding checklist is useful only when the sequence reflects the actual risks.
The process should begin by coordinating the exit, then securing identity and remote access. From there, IT should protect the device using the available management controls while Operations initiates the physical return. Once the laptop arrives, the asset should be verified, documented and routed into its next lifecycle stage.
The most important shift is to stop treating “get the laptop back” as the entire offboarding process.
- A laptop can be physically recovered while an employee still has access to a VPN.
- A user’s account can be disabled while a company laptop remains unrecovered.
- A laptop can arrive at a warehouse while nobody knows whether its data has been sanitized.
- A good remote offboarding process closes all three gaps: access, data and hardware.
For teams managing a handful of employees, that can be handled manually with a disciplined checklist. As the workforce becomes more distributed, however, the value of connecting HR events, access controls, device management and retrieval becomes much greater.
That is where lifecycle automation starts to become an operational advantage rather than simply another IT tool.
Remote Employee Offboarding Checklist: Quick Reference
Before closing an offboarding ticket, confirm:
☐ HR and IT coordinated the exit
☐ Final working time confirmed
☐ Device inventory identified
☐ SSO and email access revoked
☐ Active sessions and MFA reviewed
☐ VPN and remote access revoked
☐ Shared credentials reviewed
☐ Device locked or wiped where appropriate
☐ Return kit or prepaid label sent
☐ Shipment tracked
☐ Device received
☐ Serial number verified
☐ Condition recorded
☐ Offboarding actions documented
☐ Device routed for redeployment, repair, resale or disposal
A checklist like this is simple enough to use during an actual employee exit, while still creating the documentation and controls needed for a scalable remote IT operation.